Repository navigation
feat(web): read-only workspace activity pages - #407
Conversation


Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>

|
Warning Review limit reachedYou've used all free OSS reviews for now. Wait for the free limit to reset to keep reviewing this public repository. Next included review available in 24 minutes. View limit details
Thanks for using CodeRabbit! It's free for OSS, and your support helps us grow. If you like it, consider giving us a shout-out. Comment |


…t touching prose

Basic/Bearer now match only in Authorization headers (or a long standalone
Bearer token), so text like "Basic functionality" survives. Commands and
outputs also redact ALL_CAPS secret env assignments, credential CLI flags and
user:pass@ URLs.

Co-Authored-By: Claude Sonnet 5.5 <noreply@anthropic.com>
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>

247e74c to
fddf8f8
Compare

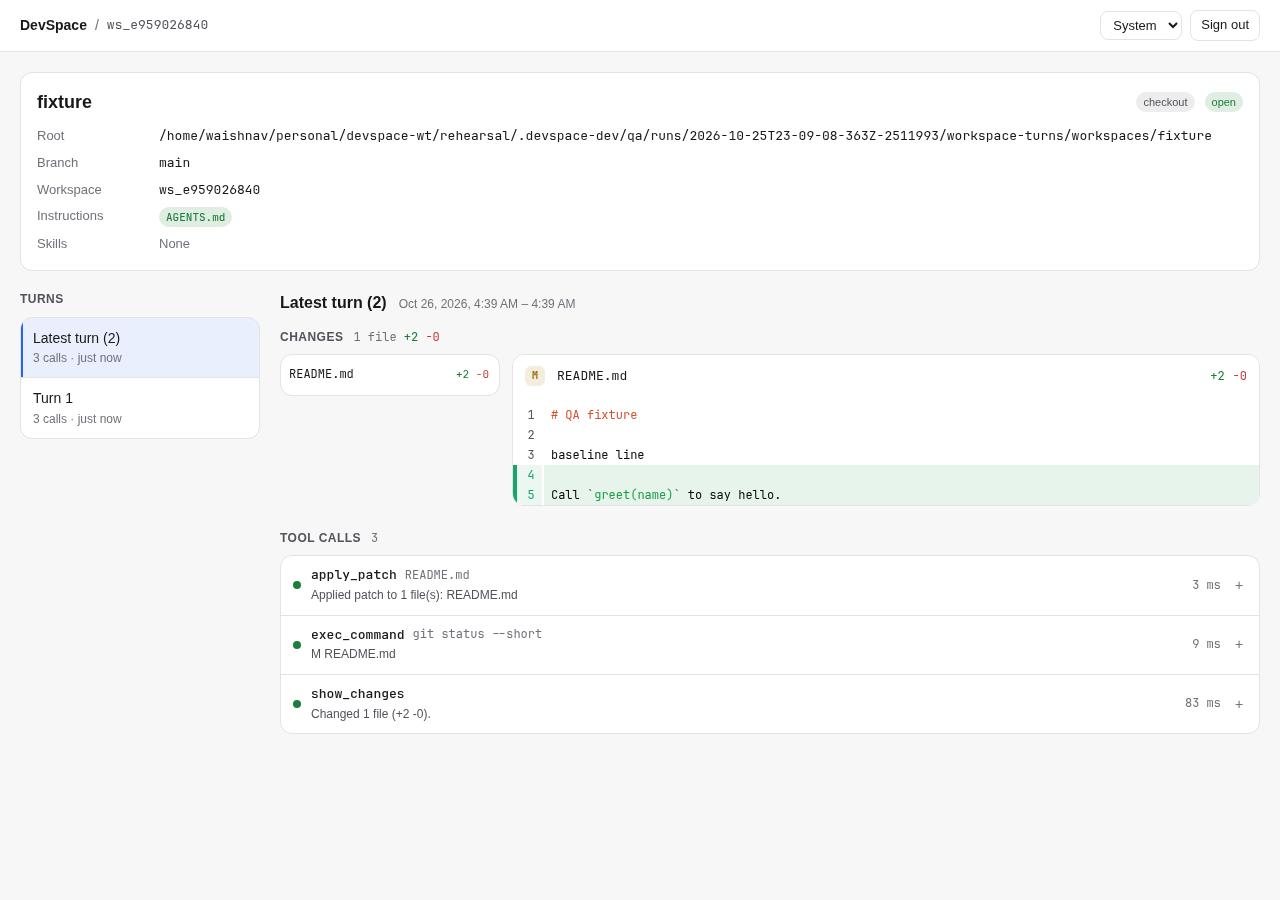
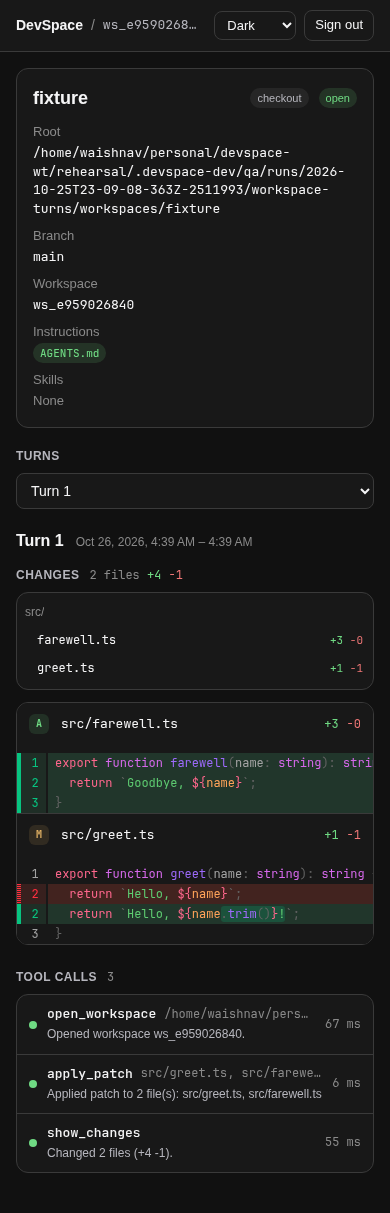
Verified on the combined v1.1 branchI built a local rehearsal branch with every v1.1 PR merged in order (#403, the small fixes, #404–#406, #408, the subagent stack #379–#384, #410, #409, #399, #341 with its migration renumbered to 14, and this PR). On it, These pages, driven with agent-browser on that branch:
|

|
@coderabbitai review |
|

DevSpace now journals every workspace's turns (#341), but there was no way to look at them. This adds read-only pages, served by the DevSpace server under
/web, for looking back at what happened in a workspace. The host is still the orchestrator; these pages never drive work.There are three views.
/web/lists open and recent workspaces with root, mode, branch, status, turn count and last activity./web/w/<workspace_id>has a header with the same details the open_workspace card shows (root, mode, branch, loaded and available instruction files, skills), the turn list on the left (latest first), and the selected turn on the right./web/w/<workspace_id>/turns/<n>shows that turn's diff from checkpoint N-1 to checkpoint N as a file tree plus diffs, then the tool calls made during the turn. Each call shows its arguments, a result summary, duration and error state, and expands. The interaction model follows t3code's diff panel. On narrow screens the turn list becomes a "Latest turn / Turn N" selector. The diff rows reuse the card's rendering:ReviewDiffFileand its CSS moved into a sharedsrc/ui/review-diff.tsx/review-diff.cssthat both the card and the pages import, so nothing is forked. The pages have their own Vite entry (vite.web.config.ts,pnpm build:web→dist/web), so the card'svite.config.tsis untouched. Workspace details come from a newWorkspaceRegistry.describeWorkspace, which reads instructions and skills without touching or reactivating the session (getWorkspacedoes both).Auth. These pages expose local code, so nothing under
/webexcept the login form and the static bundle is reachable without the owner's credential, including through a public tunnel. I reused the existing owner token instead of adding a credential./web/logintakes the owner password and creates a random session (only its hash is kept in memory, 12-hour lifetime, cleared on restart and by sign-out). The session goes in anHttpOnly; SameSite=Strict; Path=/webcookie, markedSecurewhen the request arrived over HTTPS. Login and logout are the only state-changing forms, and they accept a post only whenSec-Fetch-Site(orOriginon older browsers) says same-origin. Ten failed logins in 15 minutes lock the form, because the owner password may be user-chosen. No CORS headers are sent. Responses carryno-store,frame-ancestors 'none'and a self-only CSP. The app-wide allowed-hosts check already covers/web, and a test covers DNS-rebinding hosts. A cookie session beats putting the bearer token in the browser: script on the page can't read it, other sites can't send it, and it never ends up in URLs or history.devspace servenow printsworkspace pages: <publicBaseUrl>/web/.QA used the replay harness (#404) with a new two-turn scenario,
workspace-turns: open_workspace, apply_patch, show_changes, apply_patch, exec_command, show_changes. It ran with--serve --no-browseragainst this branch, and I drove the pages with agent-browser. The harness generates the owner token per run, so on a local, unpushed copy of the harness (qa/workspace-web) I made serve mode print the server URL and owner token. That change and the scenario are not ontest/replay-qa. QA caught one real bug: withReferrer-Policy: no-referrer, Chrome sendsOrigin: nullon form posts, so login was rejected as cross-origin. The fix is to trustSec-Fetch-Siteand useReferrer-Policy: same-origin. Unauthenticated/web/api/workspacesreturns 401 and/web/redirects (303) to login. The 390px viewport has no horizontal scroll (scrollWidth390). The console stayed clean.Not included: live updates (reload to see new turns), subagent events (the hook is in #341), and pruning of old turns or pinned refs. The Smoke check fails on every PR because of the koffi release (#403).
🤖 Generated with Claude Code